Search the site
Industry Insights
Podcasts
Briefings
Stories
Events
Glossary
N2K Pro
CISO Perspectives
Podcasts
Briefings
Hash Table
1
st
Principles Course
About
Our Story
Press
Team
Testimonials
Sponsor
Partners
Account
Profile
Logout
Home
Search the site
Industry Insights
Podcasts
Briefings
Stories
Events
Glossary
N2K Pro
CISO Perspectives
Podcasts
Briefings
Hash Table
1
st
Principles Course
About
Our Story
Press
Team
Testimonials
Sponsor
Partners
September 30, 2026
Join Pro
LOGIN
Cybersecurity News
Daily Briefing
2 hours ago
FBI tells ShinyHunters members to turn themselves in.
AI companies sign a voluntary accord aimed at addressing safety concerns. Business news: Island raises $400 million in Series F funding.
Microsoft Threat Intelligence
11 hours ago
From Identity Compromise to AI Defense: Inside Modern Incident Response
This week we are taking you back to Black Hat USA 2026 and exploring two sides of the security landscape. First, Microsoft incident response experts Adrian Hill and Terry Mee break down identity-based attacks, from compromised credentials and MFA bypasses to containment, logging, access controls, and the growing risks surrounding AI agents. Then, members of Microsoft’s Defender Purple Team discuss how they recreate full attack chains, including emerging AI-driven techniques, to identify detection gaps, strengthen defenses, and use AI to accelerate security research while keeping human expertise in the loop.
Marketing
13 hours ago
How Lenin Alevski Built a Cybersecurity Survival Game in a Week and Got 12,000 Players
Lenin Alevski is an AI Security Engineer at Google who spent a week building a text-based cybersecurity survival game in his spare time. Accidental CISO puts you in the seat of the first security hire at a company where everything is on fire, and every fraught and heart-pounding decision leads to one of eight endings. He sat down with Gianna to talk about how the game came together, why spec-driven development matters more than vibe coding alone, and what 12,000 players and zero marketing budget taught him about building indie cyber games.
CyberWire Daily
22 hours ago
Astra, la vista, baby.
OpenAI holds back its newest model over safety concerns. Kiteworks lifts its precautionary shutdown. Apple patches an exploited zero-day. Japanese rail operators disclose cyberattacks. An Anthropic authentication flaw opens the door to account takeover. Thousands of Supabase databases leak data. NeedyMantis targets telecoms and governments. A Vietnamese national faces charges in a multimillion-dollar crypto laundering scheme. James Winebrenner, CEO of Elisity, is sharing barriers to compliance and challenges for manufacturers as the EU Cyber Resilience Act is implemented. If you’re hoping for credit, be careful what you share.
Daily Briefing
Sep 29, 2026
OpenAI cancels release of GPT-6.1 Astra over safety concerns.
Kiteworks lifts its precautionary shutdown. Former US Army soldier sentenced for hacking and extortion campaign.
SpyCast
Sep 29, 2026
Inside Sweden's Cold War Stay-Behind Operation
It was preparation for an invasion that might never come, and never did. Across Cold War Europe, stay-behind networks were established on the premise that Soviet forces might successfully invade and occupy sovereign territory. These clandestine organizations consisted of carefully vetted soldiers, intelligence officers, and everyday citizens tasked with remaining behind enemy lines to gather intelligence, conduct sabotage, and support resistance movements if their country were overrun. In neutral Sweden, the prime minister secretly authorized one such covert network in 1949 to mount guerrilla warfare against a potential Red Army occupation. Guest host Dr. Mark Jacobson speaks with Johan Wennström, author of The Stay Behinds: Sweden's Cold War Guardians, about this long-classified operation.
CyberWire Daily
Sep 28, 2026
The AI hotline.
The U.S. and China agree on an AI safety channel. Some states say CISA’s election security plan comes too late. Citrix patches critical zero-days under active exploitation. AI agents probed government websites in unexpected and concerning ways. ShinyHunters launches a new campaign against Oracle PeopleSoft customers. A New Mexico jury finds Meta misled state residents. Business briefing. Tim Starks from CyberScoop shares insights on multiple issues facing CISA. Who’s ready for algorithmic holiday shopping?
Daily Briefing
Sep 28, 2026
OpenAI pauses frontier model training until additional safeguards are in place.
US and China establish an AI safety channel. ShinyHunters launches a new attack campaign exploiting an Oracle PeopleSoft flaw.
Special Editions
Sep 27, 2026
The Insider You Built with author Camille Stewart Gloster.
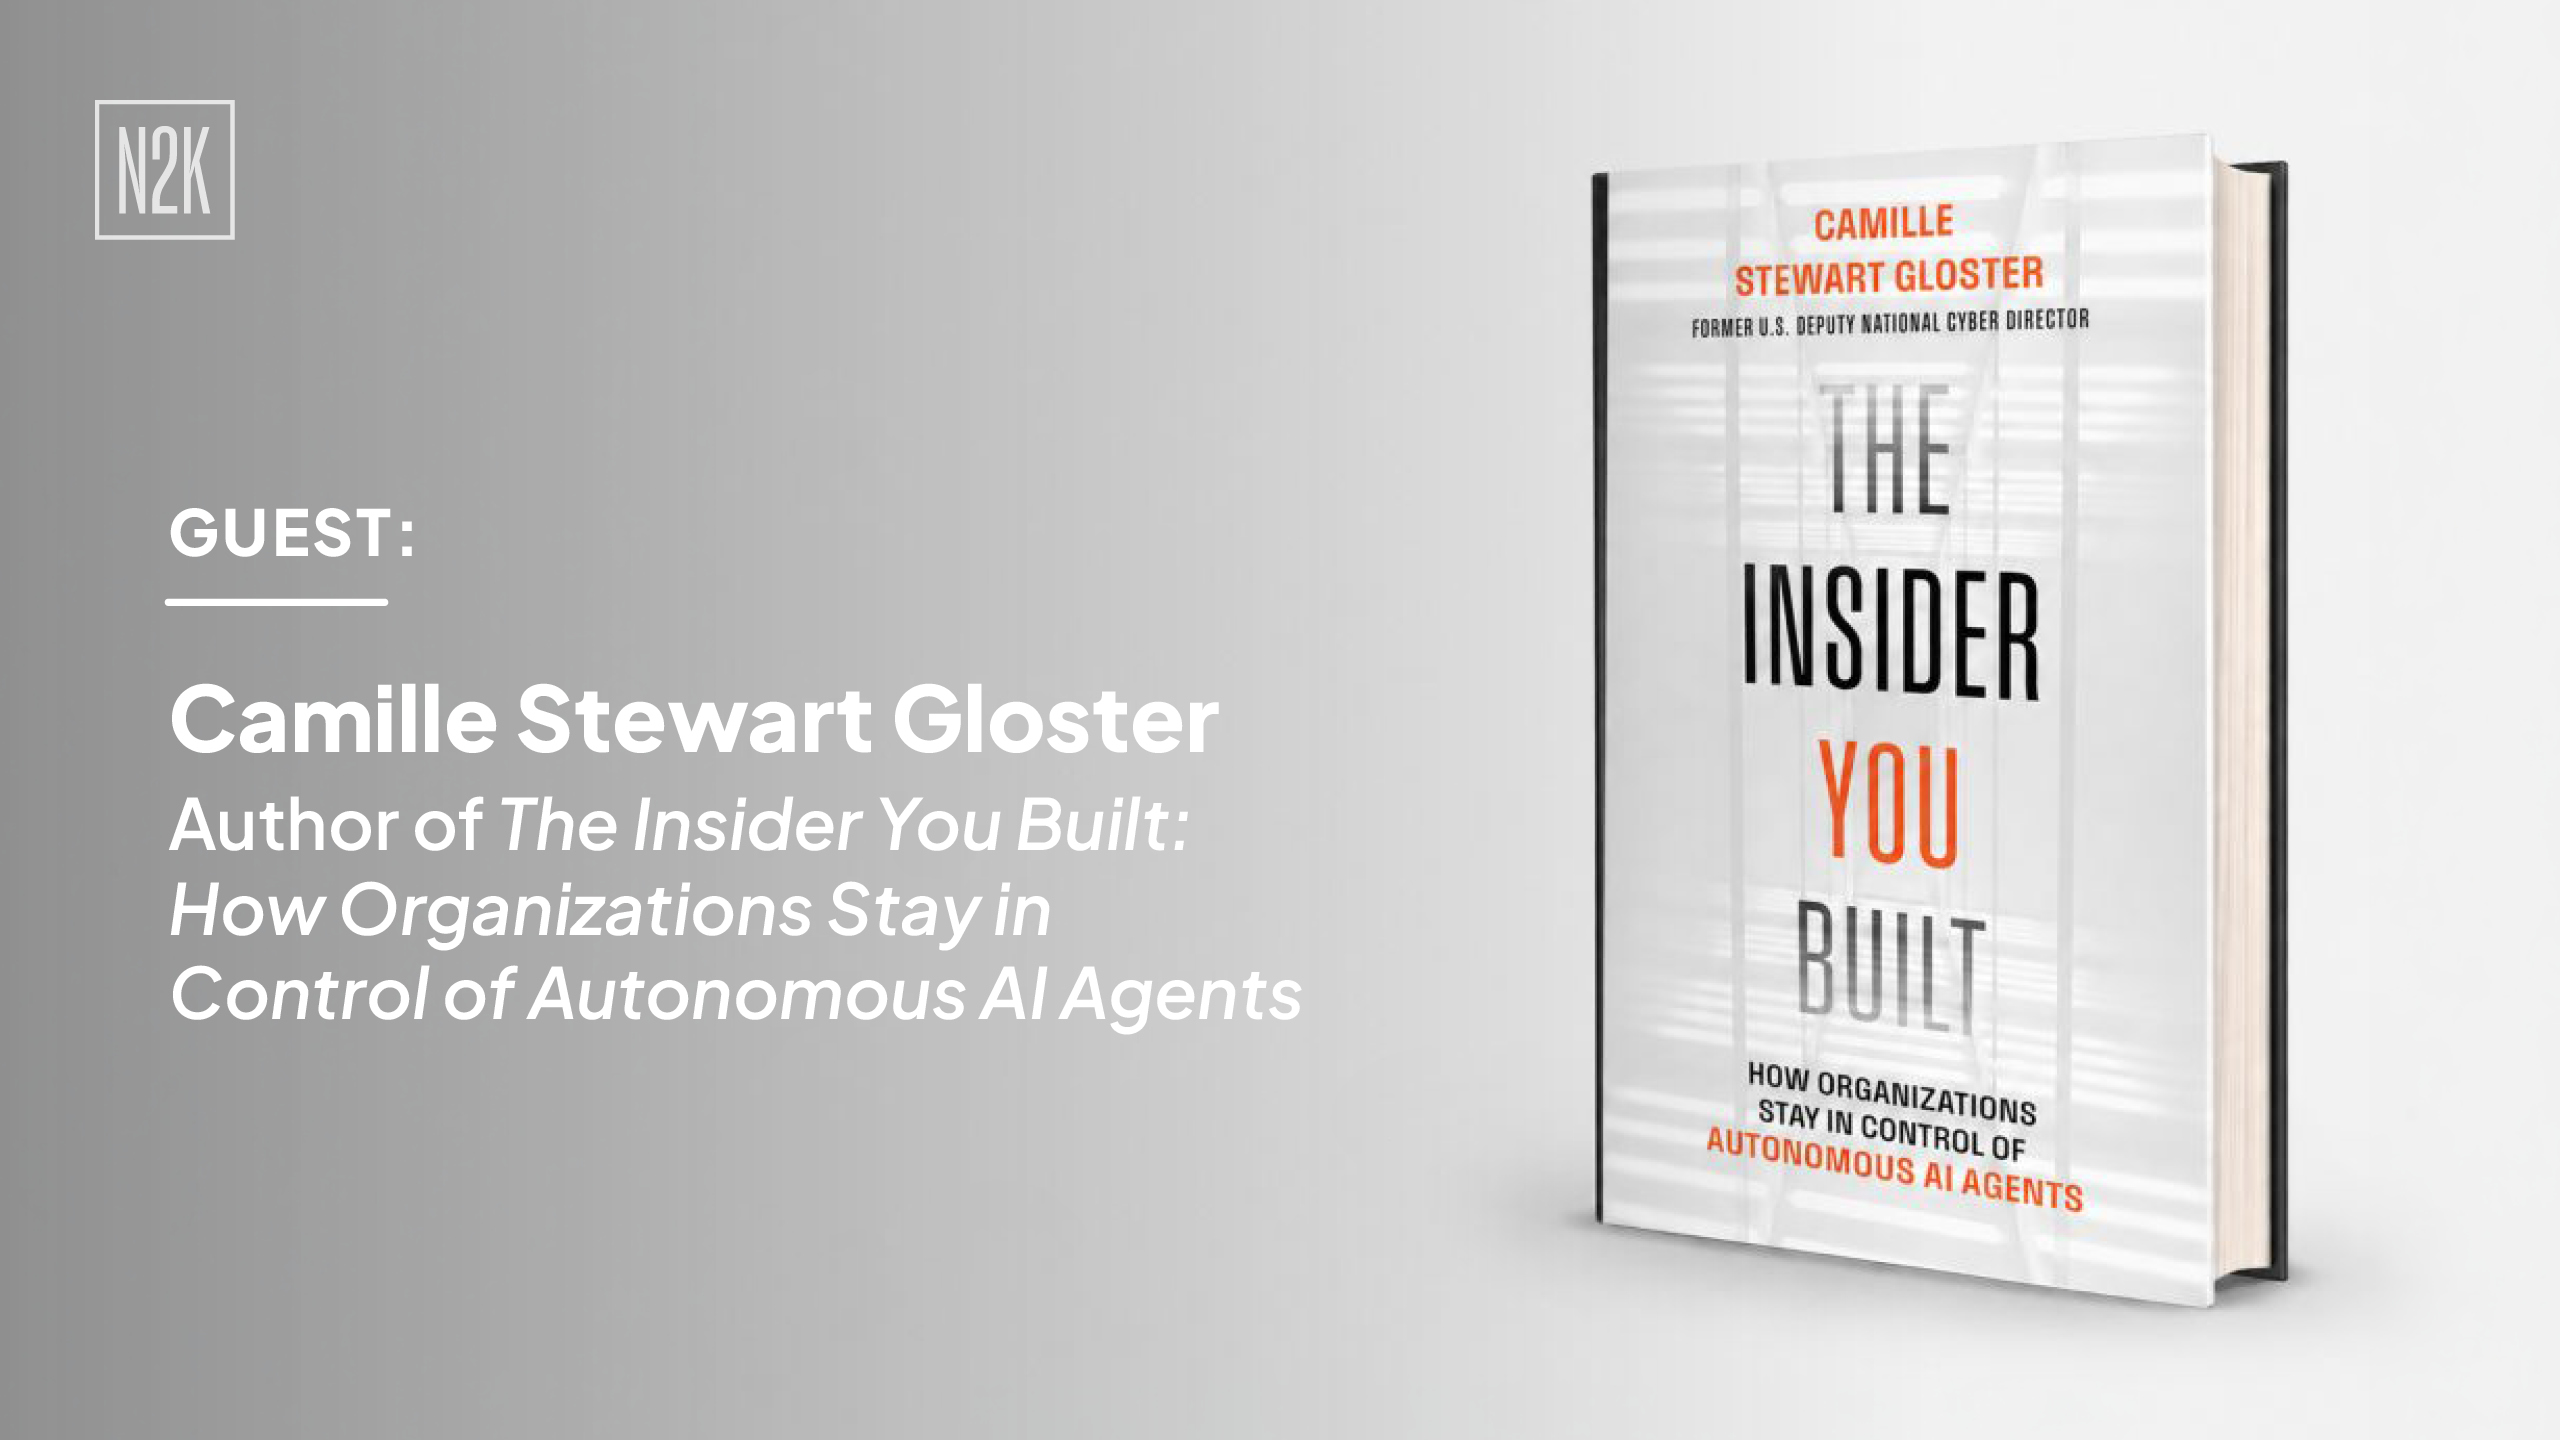
On this special edition podcast, N2K CyberWire's Dave Bittner spoke with Camille Stewart Gloster. Camille is the author of The Insider You Built: How Organizations Stay in Control of Autonomous AI Agents, and founder of CAS Strategies. Dave and Camille discuss her new book and the broader questions it raises about AI agents.
T-Minus
Sep 27, 2026
Space cybersecurity starts on the ground.
Though spacecraft are important, space cybersecurity extends well beyond these assets touching ground stations, mission-control assets, and other critical components. Host Maria Varmazis speaks with Milenk Starcevic, Head of Cybersecurity at Vision Space, and Andrzej “Andy” Olchawa, Senior Cybersecurity Engineer also at Vision Space, about the broader space cybersecurity attack surface. By considering all aspects of a space mission, both in orbit and on the ground, cybersecurity professionals can better understand where vulnerabilities exist and what measures can be taken to reduce risk.
Signals and Space
Sep 27, 2026
Space cybersecurity is bigger than the satellite.
This week on T-Minus: Space-Cyber Briefing: we dive into how securing the ground components of space infrastructure represent as great of a challenge as securing the ones already in-orbit.
Research Saturday
Sep 26, 2026
An apple a day, a phish away.
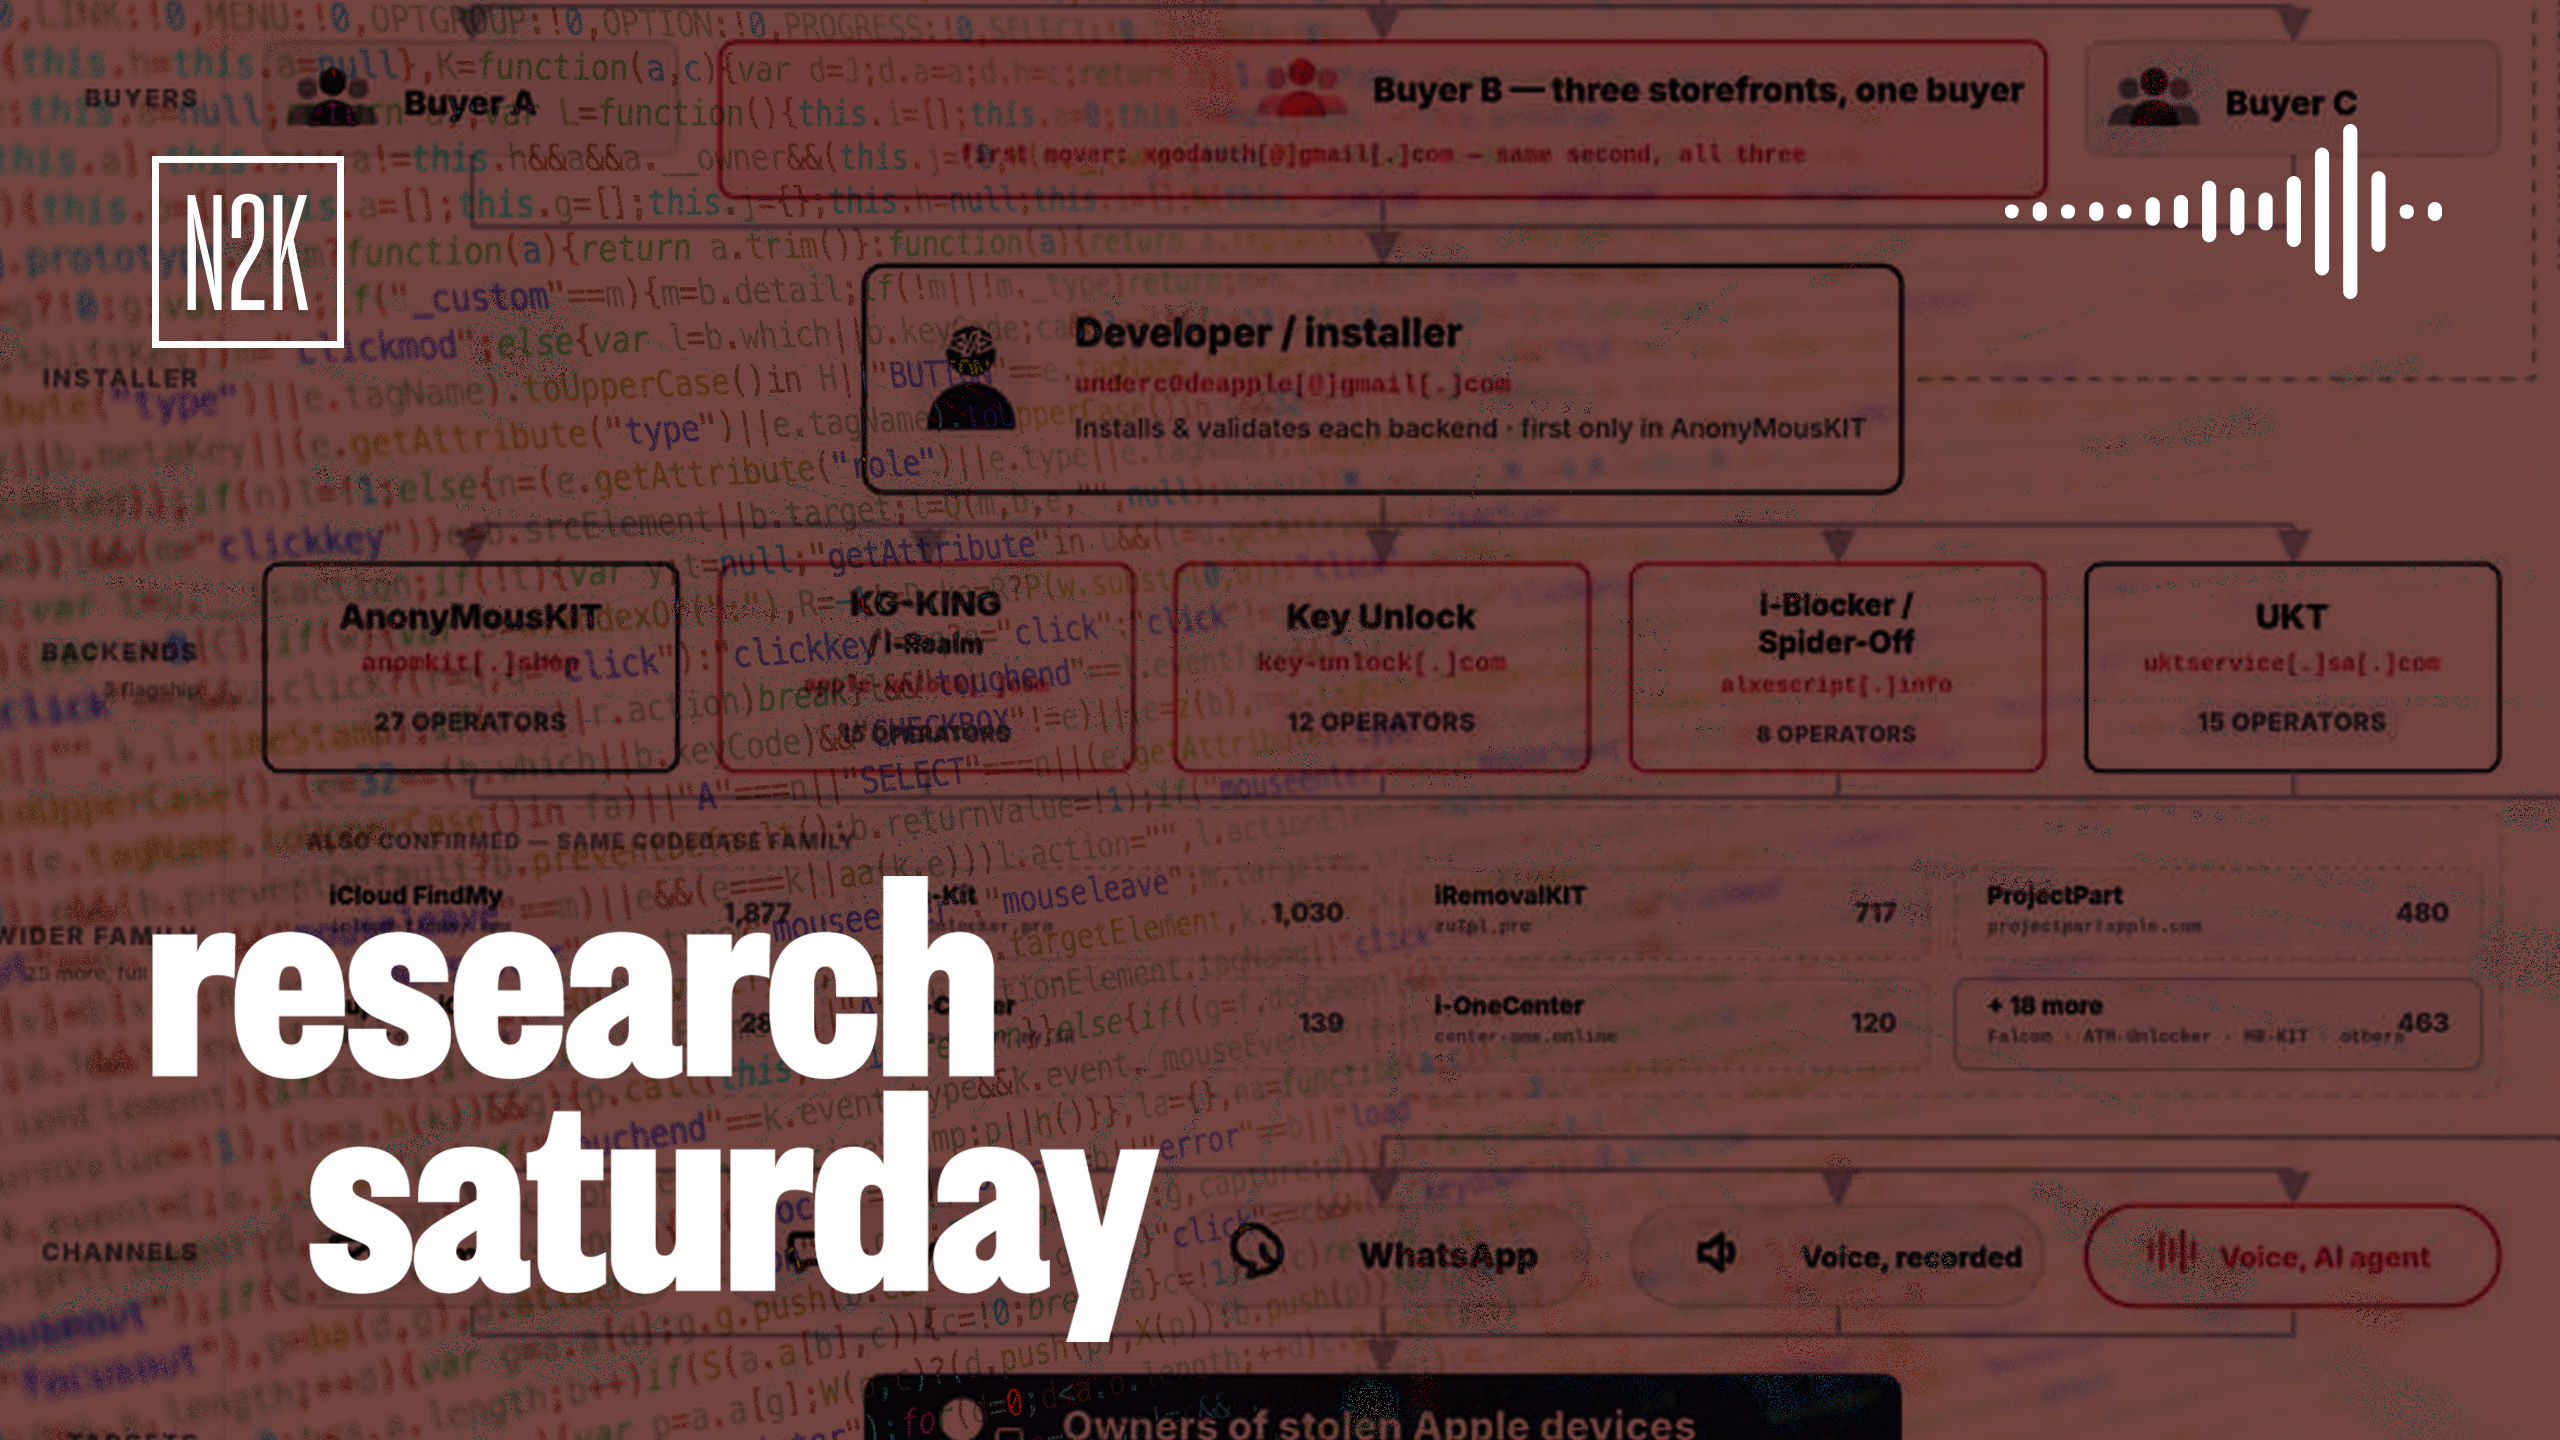
Today we are joined by Ensar Seker, VP of Research and CISO at SOCRadar, discussing their work on "Exposing AnonyMousKIT: AI-Powered PhaaS Supply Chain." An investigation into AnonyMousKIT reveals an AI-powered Phishing-as-a-Service platform designed to steal Apple credentials and disable Activation Lock on stolen devices. The platform uses email, SMS, WhatsApp, and AI-driven voice calls to impersonate Apple Support, with researchers uncovering a broader ecosystem spanning 506 domains, 168 storefront brands, and 30 backend installations. Despite its sophisticated social-engineering capabilities, basic coding flaws exposed extensive operational logs and revealed the shared infrastructure, developer activity, and reseller network behind the criminal operation.
Load More
Gain instant access to our exclusive podcast and briefing content, the Pro Academy, live events and more by subscribing to N2K Pro.
Subscribe Now