

An apple a day, a phish away.


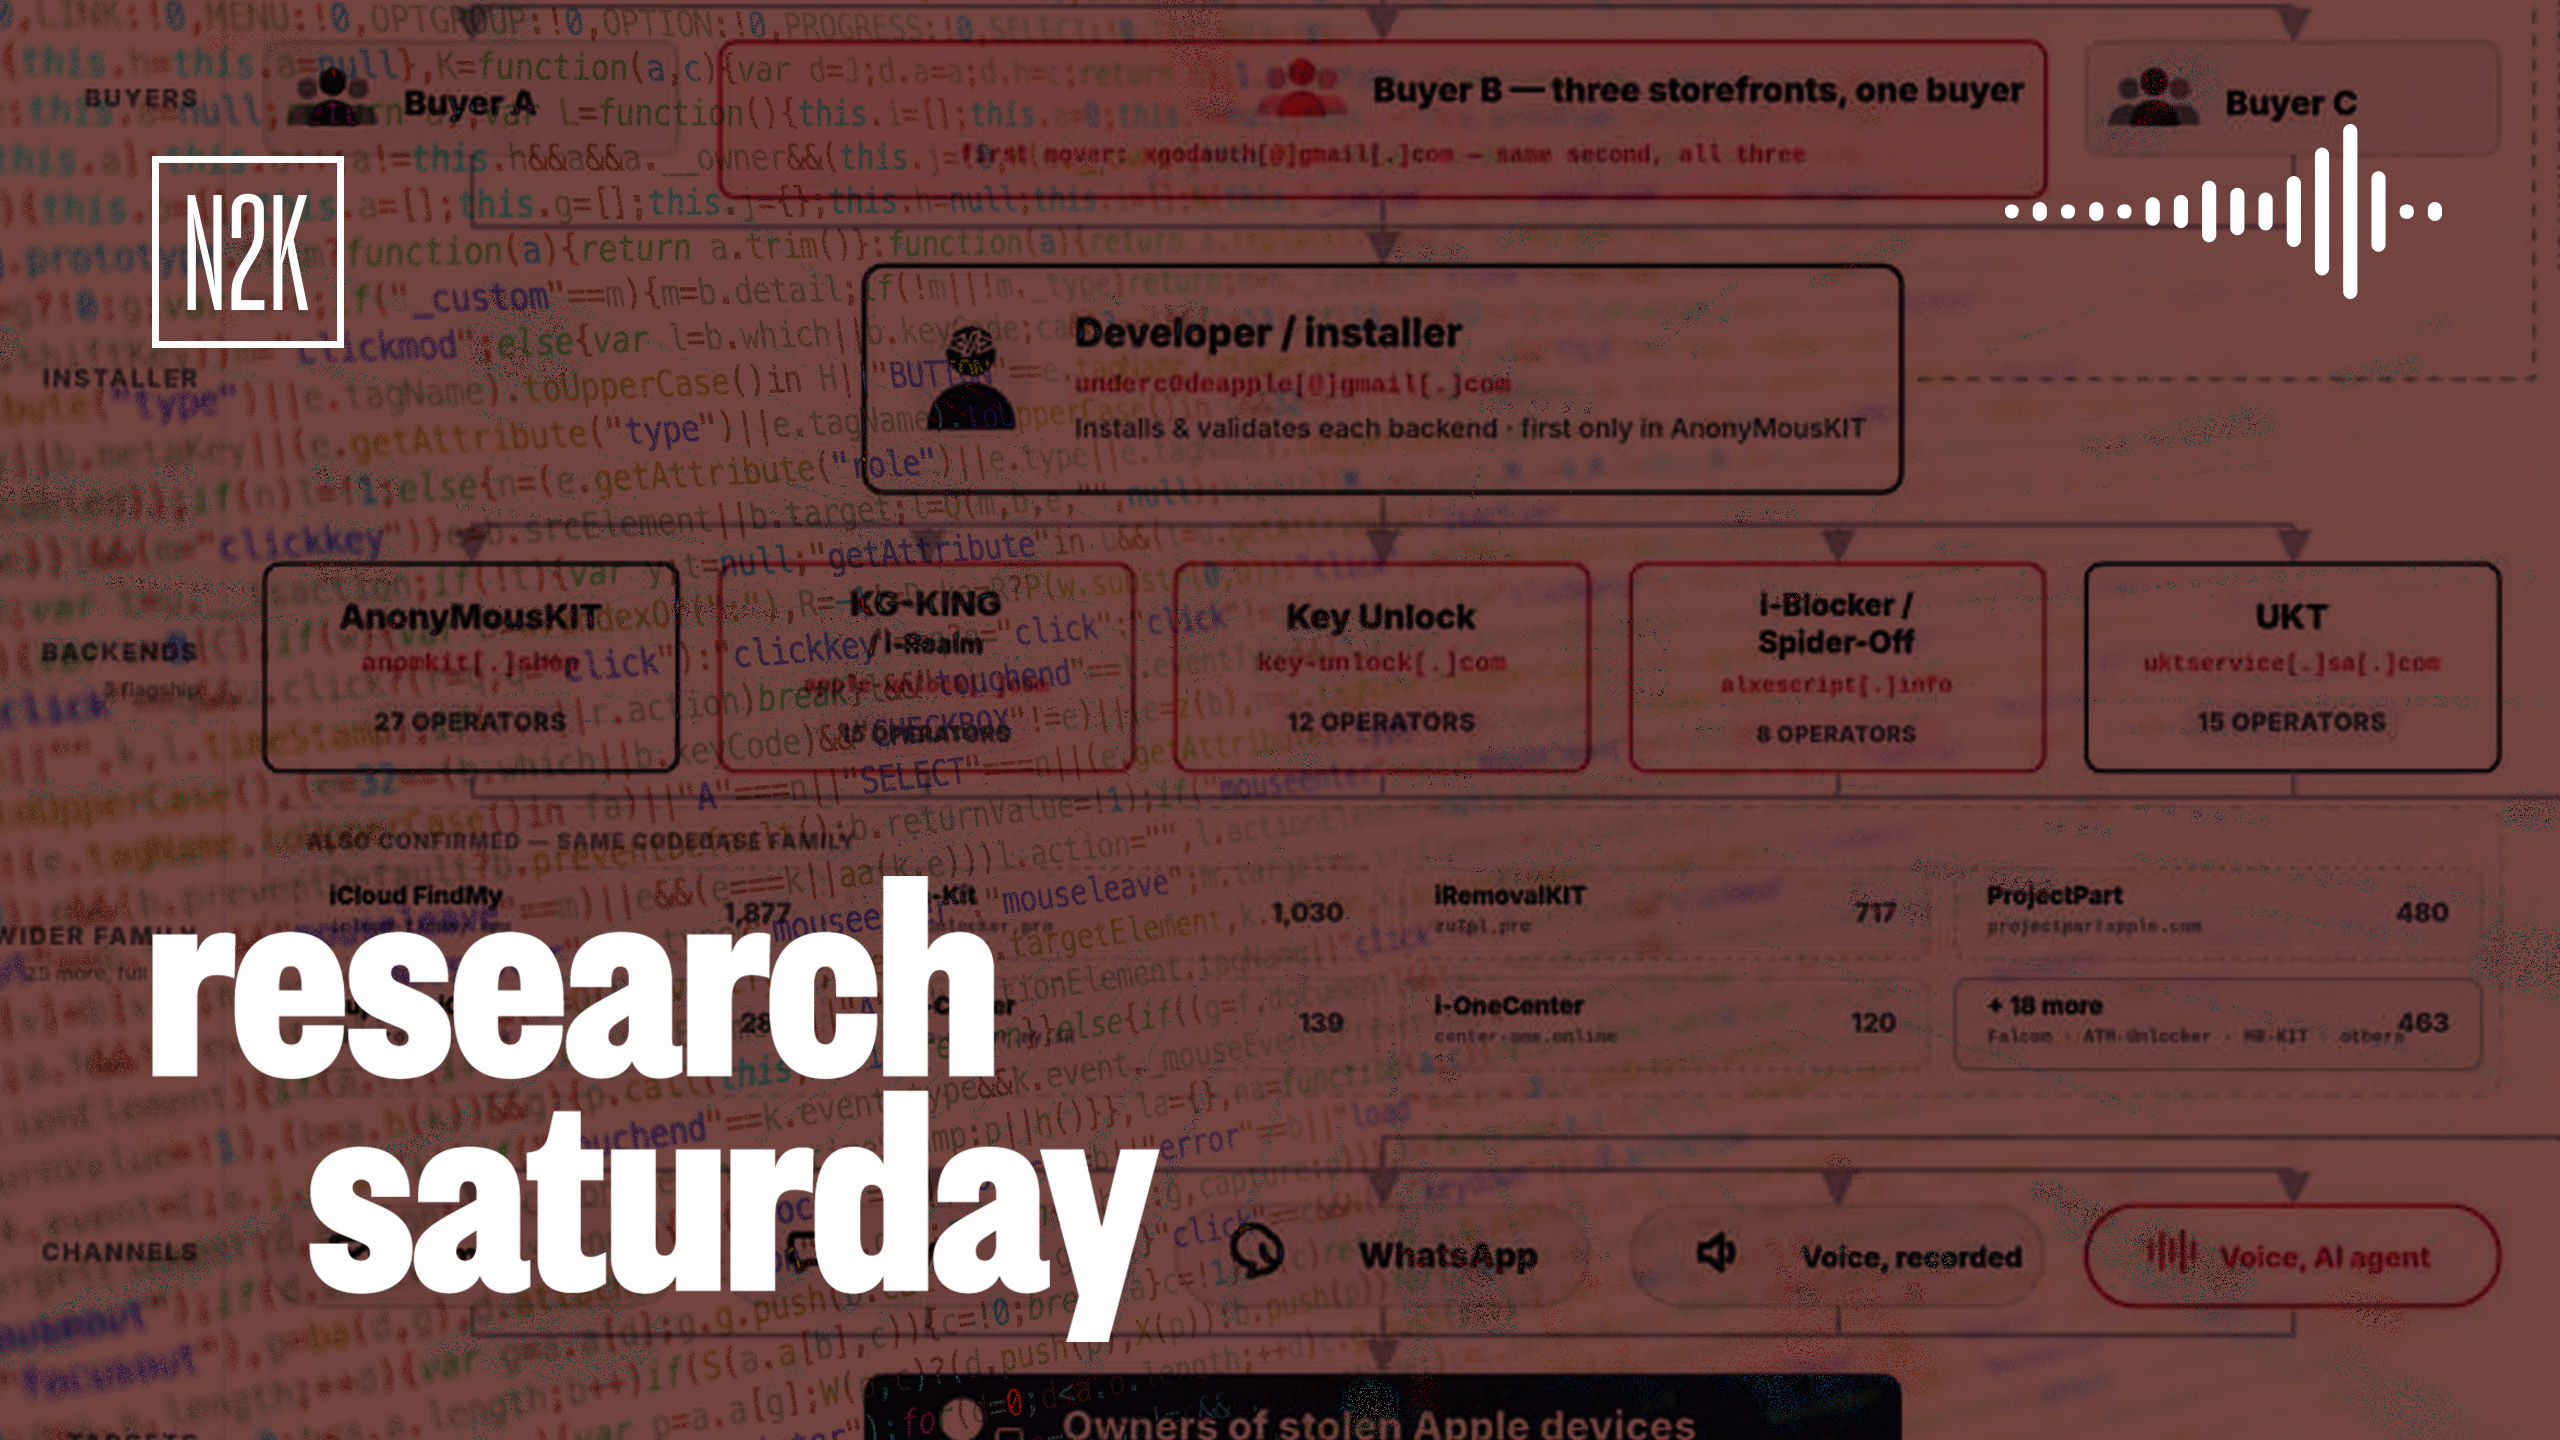
Today we are joined by Ensar Seker, VP of Research and CISO at SOCRadar, discussing their work on "Exposing AnonyMousKIT: AI-Powered PhaaS Supply Chain." An investigation into AnonyMousKIT reveals an AI-powered Phishing-as-a-Service platform designed to steal Apple credentials and disable Activation Lock on stolen devices.
The platform uses email, SMS, WhatsApp, and AI-driven voice calls to impersonate Apple Support, with researchers uncovering a broader ecosystem spanning 506 domains, 168 storefront brands, and 30 backend installations. Despite its sophisticated social-engineering capabilities, basic coding flaws exposed extensive operational logs and revealed the shared infrastructure, developer activity, and reseller network behind the criminal operation.