

The wrong kind of access.


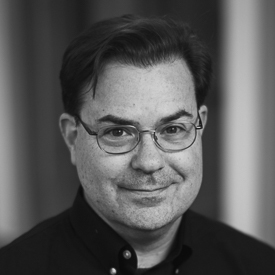
Dan Lisichkin, AI Security Researcher from Pillar Security, discussing their work on "A WIF Of Fresh Access, How a GitHub Issue on Gemini-CLI Led to GCP Project Compromise." Researchers at Pillar Security uncovered a vulnerability in Google’s Gemini CLI workflows that could allow an attacker to turn a malicious GitHub issue into remote code execution and gain elevated access to a Google Cloud Platform (GCP) project.
The exploit chain combined a misconfigured tool allowlist that allowed unrestricted command execution with exposed Workload Identity Federation credentials and overly broad service account permissions, potentially enabling attackers to impersonate privileged accounts. Google promptly addressed the issues by tightening tool restrictions, blocking the agent’s access to credential files, and limiting service account impersonation permissions, highlighting the risks of connecting AI agents to untrusted input and sensitive infrastructure.